Encryption's Hidden Role in Aligning Charge Sequences with Consumption Metrics for Tiered Platforms
Written by Viktor Wolf · Oct 2, 2026
Encryption's Hidden Role in Aligning Charge Sequences with Consumption Metrics for Tiered Platforms
Encryption serves as a foundational mechanism that protects data integrity when charge sequences must match consumption metrics across tiered platforms, and it operates quietly behind the scenes in systems where usage data drives billing calculations. Tiered platforms often rely on real-time or periodic consumption measurements to determine which pricing level applies, and any discrepancy between recorded usage and applied charges can lead to compliance issues or revenue leakage. Researchers have documented how cryptographic techniques safeguard the transmission and storage of these metrics so that automated charge sequences remain accurate and unaltered during processing.
Core Components of Charge Alignment in Tiered Systems
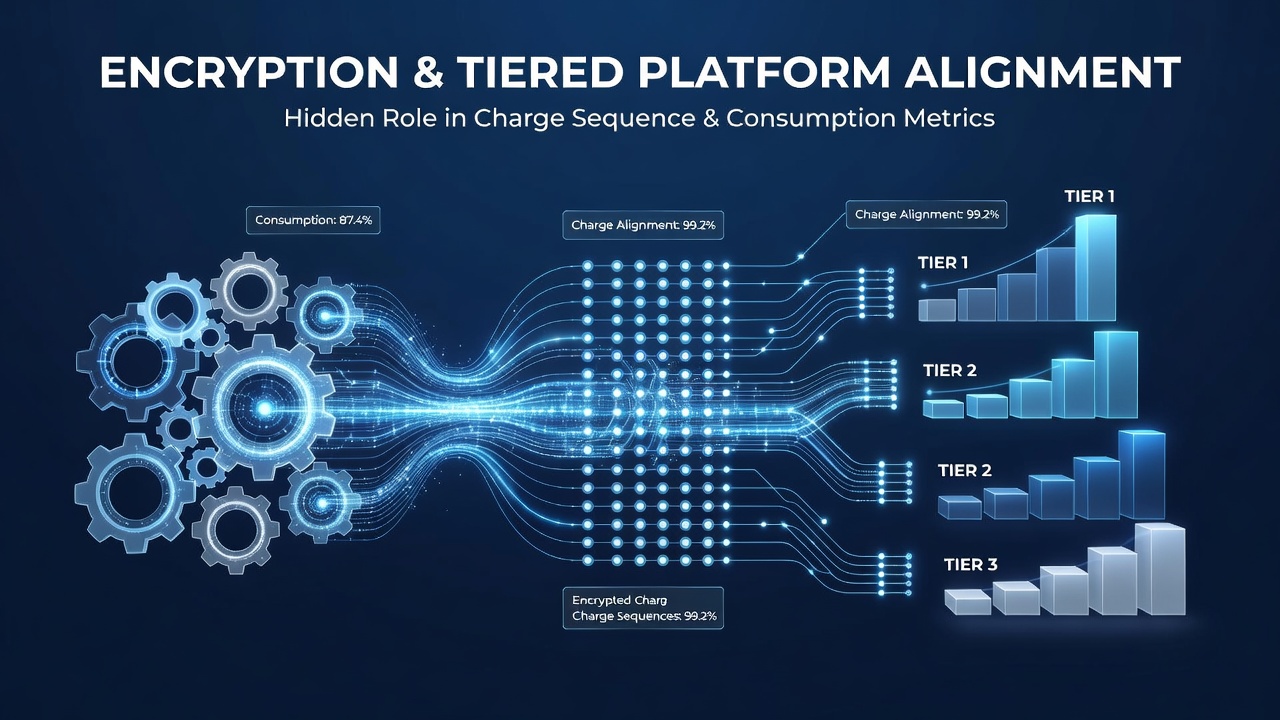
Consumption metrics originate from usage meters that track access levels, data volumes, or feature engagements, while charge sequences represent the ordered application of rates based on those metrics within predefined tiers. Observers note that without protective layers, these data points face risks during transfer between customer interfaces, internal ledgers, and external gateways. Encryption protocols such as AES-256 for data at rest and TLS 1.3 for transit ensure that consumption figures reach billing engines without interception or modification, and studies from technical standards bodies show this protection directly supports sequence integrity. Data indicates that platforms processing thousands of transactions daily depend on these methods to maintain consistency between metered input and output charges.
Technical Pathways for Secure Metric Synchronization
Encryption keys manage access controls that allow only authorized components to decrypt and reconcile usage logs with charge triggers, and this process occurs through hashed identifiers that link individual consumption events to specific tier thresholds. Those who have examined billing architectures find that asymmetric encryption often handles initial authentication steps, while symmetric methods secure bulk metric payloads during batch processing. In one documented case, experts at a research institution tracked how encrypted audit trails prevented drift between usage spikes and corresponding charge applications across multi-region deployments. Platforms integrate these layers into API endpoints so that consumption data flows into charge engines only after verification steps confirm data origin and completeness.
What's interesting is the way end-to-end encryption supports cross-system validation without exposing raw metrics to intermediate services, and this becomes especially relevant when tiered platforms operate under regulatory frameworks that mandate data protection during financial calculations. Figures from industry reports reveal that organizations adopting unified encryption standards experience fewer mismatches in recurring charge logs tied to variable consumption patterns.
Compliance and Data Lineage Considerations
Regulatory requirements in multiple jurisdictions emphasize the need for verifiable data lineages from usage events to final charges, and encryption provides the tamper-evident properties that satisfy these demands. According to guidelines published by the National Institute of Standards and Technology, cryptographic hashing combined with encryption creates immutable records that platforms can reference during audits of tiered billing accuracy. Platforms in regions following similar standards, such as those outlined by Australia's Information Security Manual, apply comparable techniques to ensure consumption metrics remain aligned with charge sequences even when data crosses organizational boundaries.
People who manage these systems often discover that key rotation schedules and certificate management directly influence the reliability of metric-to-charge mapping, because expired or compromised keys can interrupt sequence validation processes. Evidence suggests that automated key lifecycle tools integrated with billing software reduce such interruptions while maintaining compliance with data residency rules. In October 2026 updates to certain international data protection frameworks are scheduled to take effect, prompting platforms to review encryption configurations that support consumption-based charge alignment.
Integration Patterns Across Platform Ecosystems
API connections between metering services and billing modules frequently incorporate encrypted payloads that carry both raw consumption figures and derived tier assignments, and this approach prevents unauthorized alterations during the handoff. Observers have noted that tokenization sometimes works alongside encryption to obscure sensitive identifiers while still allowing charge sequences to reference the correct metrics. Research indicates that platforms using these combined methods report improved synchronization between usage peaks and applied rates, particularly in environments where consumption fluctuates across multiple tiers within a single billing cycle.
One study revealed that encryption overhead remains minimal when hardware acceleration handles cryptographic operations, allowing real-time alignment without introducing latency into charge generation. Those who've implemented such systems find that centralized key management services simplify oversight across distributed tiered platforms, ensuring consistent application of security policies to all metric and charge data flows.
Conclusion
Encryption underpins the reliable connection between consumption metrics and charge sequences in tiered platforms by protecting data integrity and supporting audit requirements throughout the billing lifecycle. Platforms that maintain strong cryptographic practices continue to demonstrate measurable alignment between usage records and applied charges, and ongoing standards development provides additional frameworks for these implementations. Data from regulatory and technical sources confirms that these methods remain central to accurate, secure operations in consumption-driven environments.